56 / Cybersecurity
Offensive Security & Red Teaming
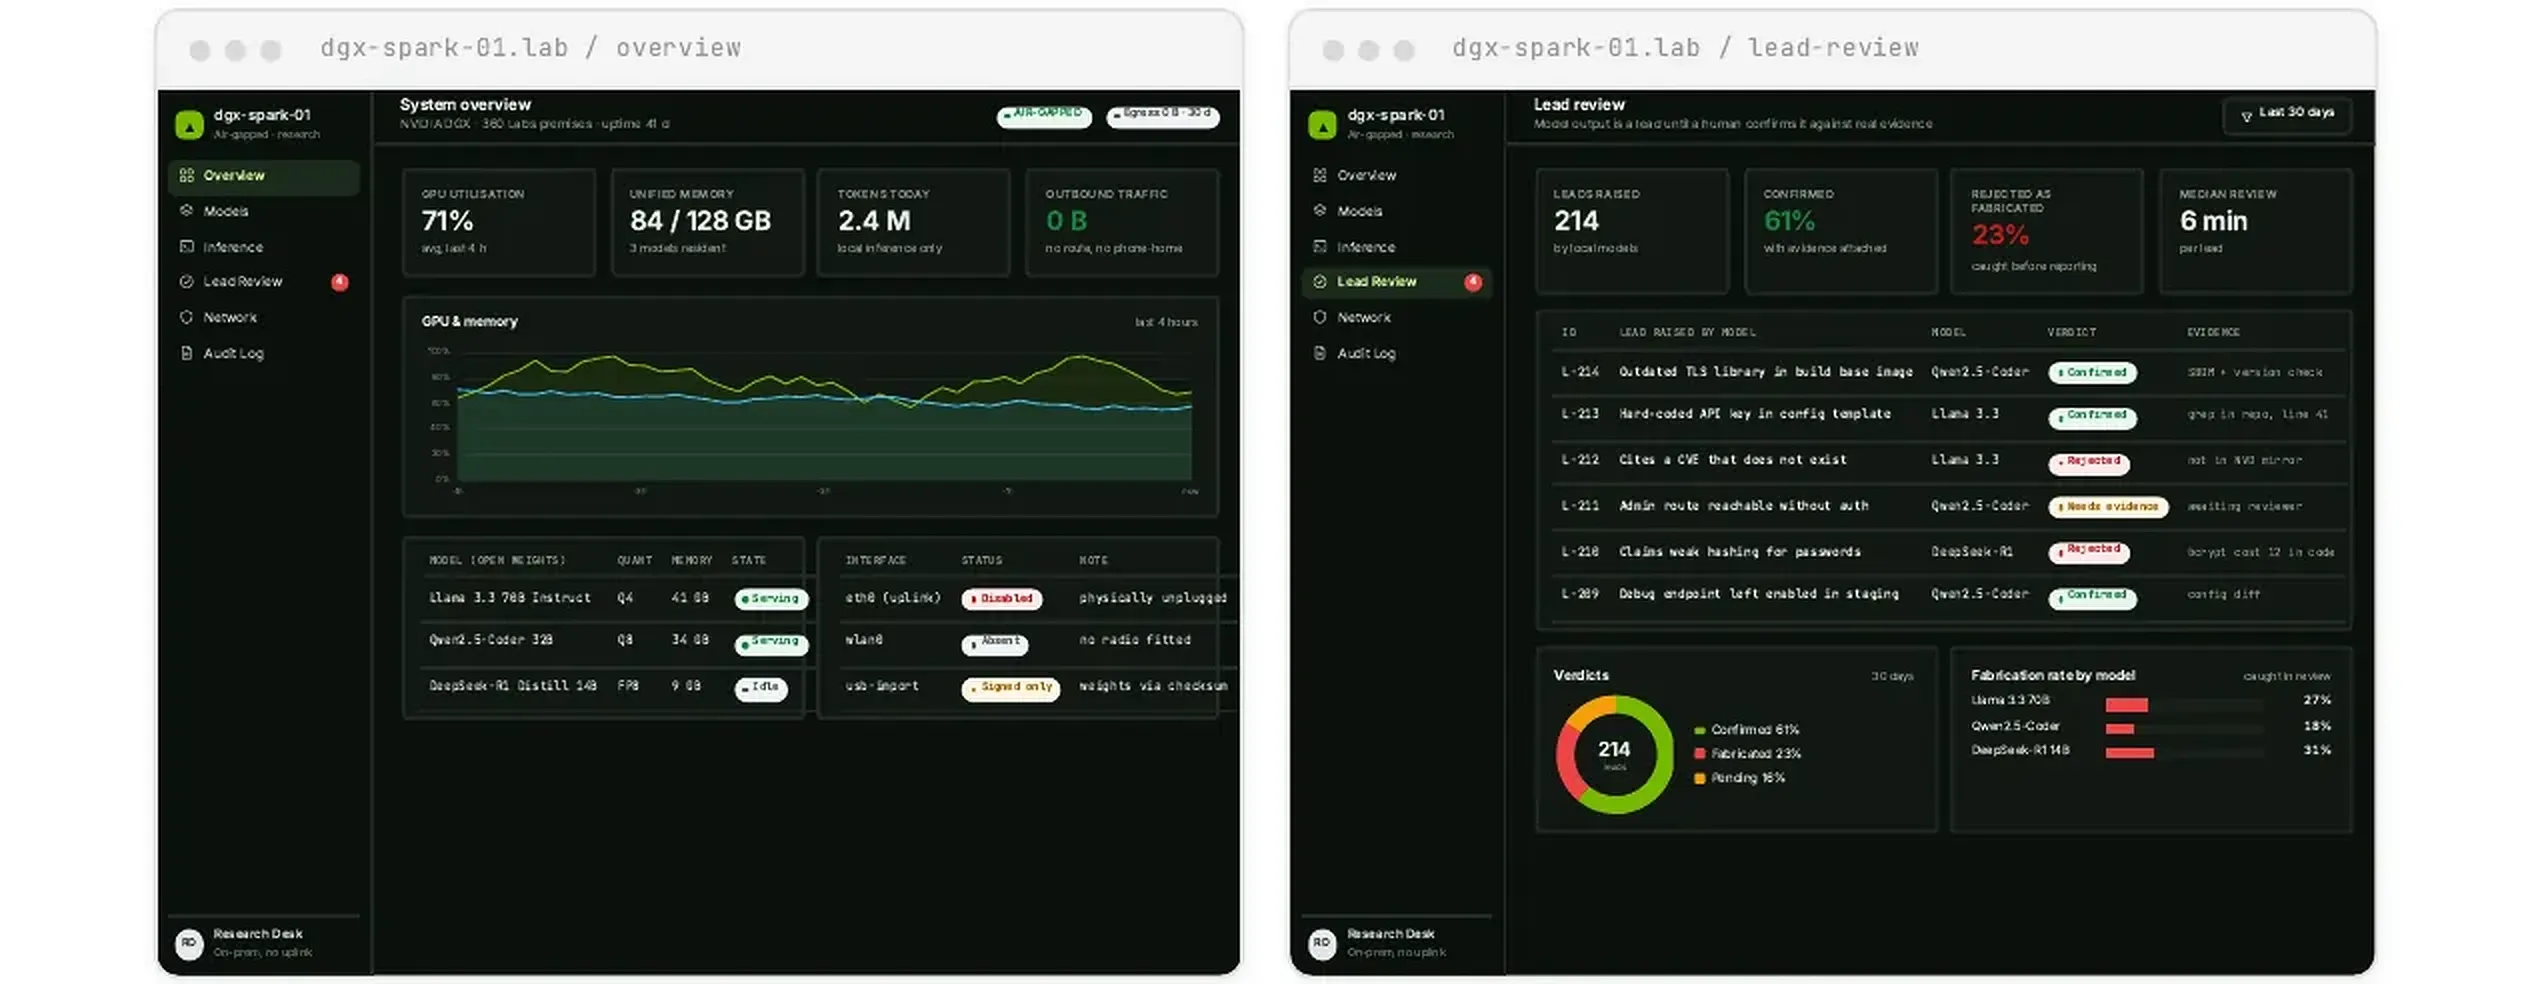
We run authorised penetration tests and red-team assessments on applications before they ship, finding and fixing the serious holes, and we do it on our own hardware so the attack data never goes to anyone else's cloud.
- Built by
- 360 Labs Security Research (Authorised Assets Only)
- Stack & approach
- CybersecurityVAPTRed TeamingAir-GappedResponsible Disclosure
The problem
Applications handling sensitive data need rigorous security testing before launch, but commercial AI tooling refuses offensive-security work, and sending attack data and findings to a third-party cloud is itself a risk.
Solution & architecture
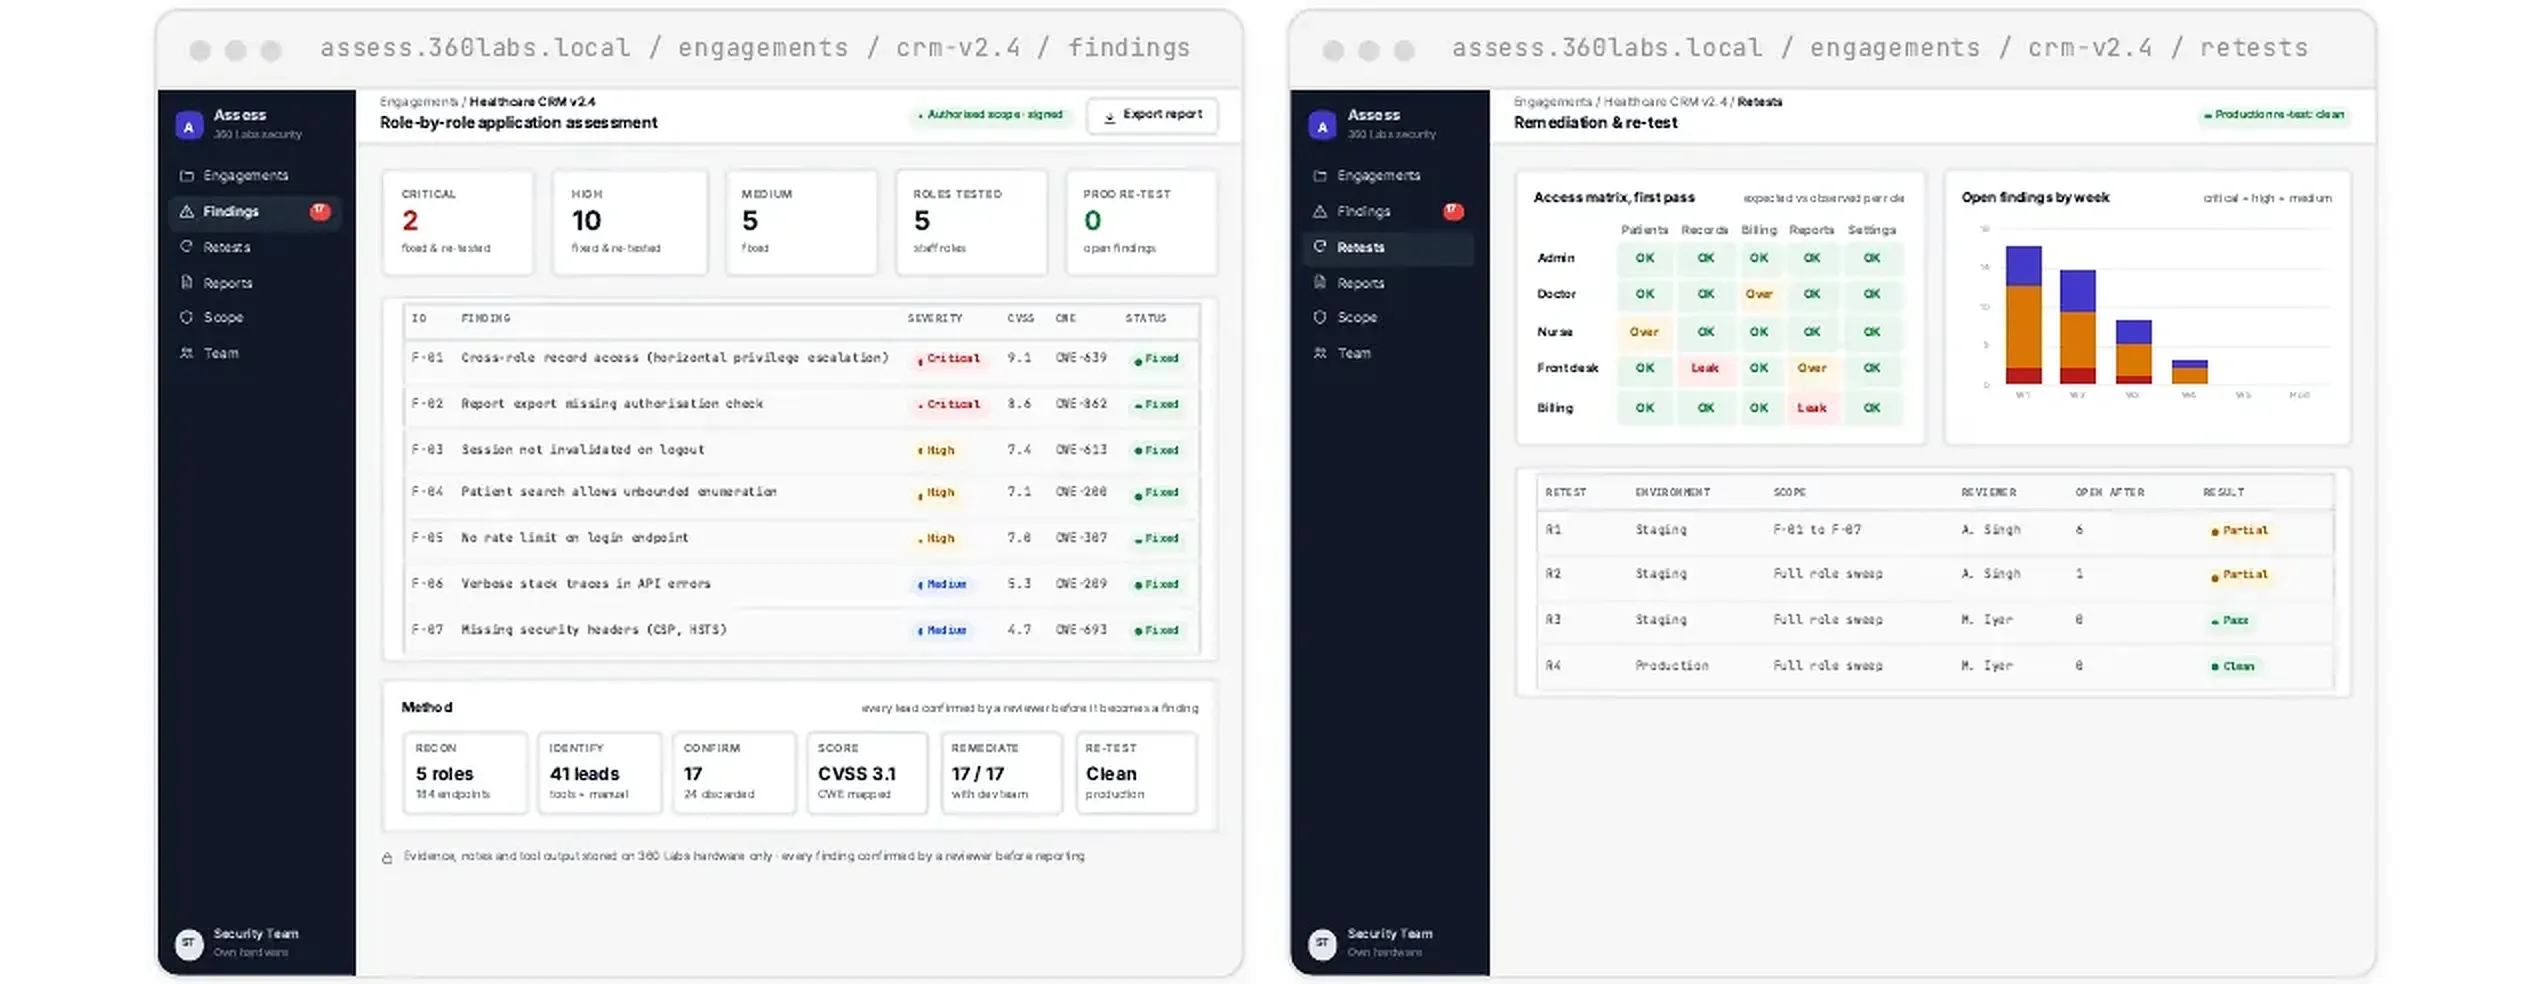
360 Labs runs authorised penetration tests and red-team assessments entirely on its own hardware. A healthcare CRM was tested role-by-role across 5 staff roles, every finding confirmed against real tool output and remediated. Methodology is deliberately human-reviewed: recon, identify, score, remediate, with automated output treated as a lead, not a finding, and only non-destructive proof-of-concept permitted on in-scope assets.
Why it is built this way
Own-hardware testing
Attack data never leaves the premises
Authorised assets only
Scope limited to what we own or are approved to test
Leads, not findings
Every claim confirmed before it is reported